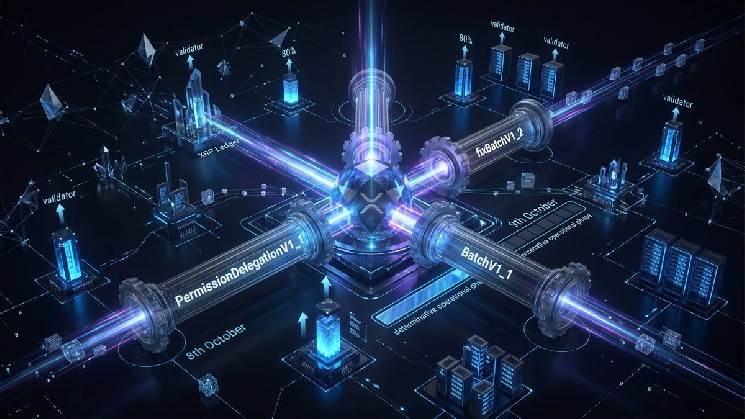

Technical data from XRPL indicates that the PermissionDelegationV1_1 amendment introduces a granular account authorization framework. Under this mechanism, a primary address can grant specific permissions to secondary accounts without compromising or transferring its master private keys.
This architectural enhancement addresses the operational demands of institutional participants. Industry analysts note that this functionality will enable banks and stablecoin issuers to segregate compliance, payment, and custody responsibilities across separate wallets. The deployment of this feature regained momentum after a temporary drop in validator support previously reset the mandatory countdown clock.
New Atomic Capabilities and Security Patches for Validators
The second deployment phase focuses on batch processing. The BatchV1_1 amendment enables the grouped execution of up to eight transactions in a single batch with atomic guarantees, meaning all operations within the set are confirmed simultaneously, or the entire batch is rejected if any single transaction fails.
This technical feature has drawn strong interest from developers building settlement engines and atomic swap solutions. Originally, the validator community anticipated activating this feature in September. However, fluctuations in the consensus percentage pushed the final confirmation window back to October 9.
Alongside this functionality comes a critical security fix. The XRPL engineering team released client software version xrpld 3.4.1 after identifying vulnerabilities in the codebase, formally integrating the fixBatchV1_2 patch.
Infrastructure operators running obsolete software builds at the time of deployment will enter an amendment blocked state. According to Ripple documentation, these nodes will lose the ability to track the general ledger consensus until they complete the software migration.
The XRPL technical governance model requires maintaining validator support above 80% for two continuous weeks to apply amendments to the mainnet. If this threshold holds through the close of the target window on October 9 at 14:46 UTC, all three implementations will become permanently active at the base layer.
